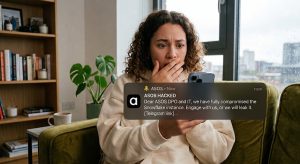
This morning, Tuesday October 6, 2026, thousands of ASOS app users across the UK unlocked their phones to an alarming message pushed directly from the fast-fashion retailer’s official app.
The notification, bearing the title “ASOS HACKED”, bypassed standard promotional channels and directed an extortion threat straight to the company’s internal IT leadership:
“ASOS HACKED”
“Dear ASOS DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it.”
The alert included a direct link inviting company officers and millions of unsuspecting shoppers to join a Telegram channel to negotiate.
Immediate Fallout: Social Media Panic and Market Reaction
Within minutes of the push alert broadcasting around 10:01 AM BST, screenshots flooded X (formerly Twitter) and Reddit. Confusion quickly turned to concern over the security of saved payment cards, home addresses, and order histories.
Downdetector logged hundreds of user reports within the first hour. The financial markets reacted rapidly to the breach notification: ASOS shares on the London Stock Exchange dropped by over 10% to 12.5% within hours of the incident.
What Was Affected?
ASOS quickly issued guidance across its social channels and customer support portals, advising customers not to click or engage with the Telegram link contained in the notification.
The company subsequently restricted access to its notification delivery systems and launched an investigation alongside third-party cybersecurity specialists and relevant authorities.
How Did Threat Actors Hijack the App Notifications?
While investigations remain active, security analysts highlight that sending a push notification directly through a brand’s verified app typically stems from compromised API credentials or access keys in third-party messaging and customer engagement platforms.
The perpetrators specifically targeted Snowflake, a cloud-based data platform widely used by enterprise brands to store and analyse customer demographic and behavioural data. Attackers leveraged the push notification system to execute a public, high-visibility extortion campaign aimed at pressuring ASOS’s Data Protection Officer (DPO) and IT security team.
Advice for ASOS Customers
If you received the notification on your device:
Monitor official ASOS channels (app notices, official website, and verified social media accounts) for verified security updates.
Do not click the Telegram link or interact with any external communications linked to the message.
Beware of follow-up phishing attempt messages via email, SMS, or direct messages pretending to offer account recovery or support.
Update your password as a general precaution, especially if you reuse credentials across multiple sites.